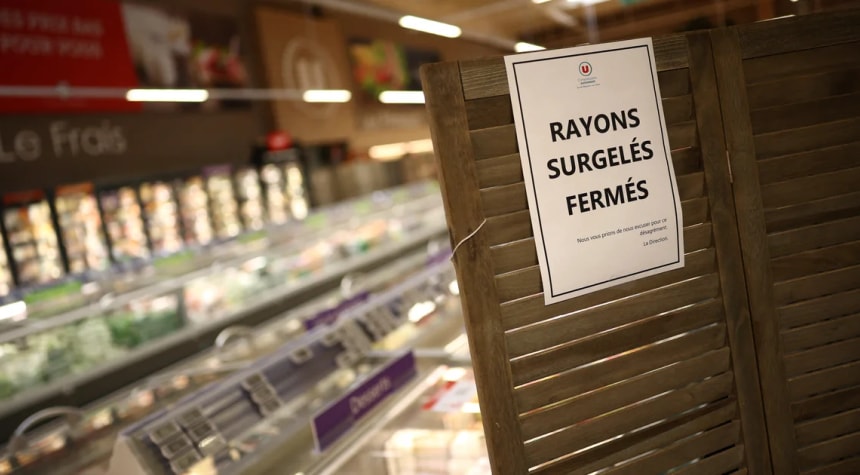
The Islamic Revolutionary Guard Corps just proved they can spoil your dinner from halfway across the world, and if that doesn’t terrify you, you haven’t been paying attention. French prosecutors announced Monday that Iran’s cyber thugs orchestrated a coordinated attack on 700 grocery stores across France last October, remotely hijacking refrigeration systems and causing massive food spoilage. Oh, and they started about twenty fires in the process. Just your average Tuesday for the IRGC, apparently.
Here’s what actually happened. Iranian hackers gained control of commercial refrigeration units and forced them into indefinite defrost cycles while simultaneously disabling every safety alert designed to prevent exactly this nightmare scenario. Temperatures soared. Food rotted. Fires broke out. The regime’s cyber operatives sat somewhere in Tehran, typing commands in Farsi, and watched French supermarkets burn through inventory and cash.
This wasn’t some isolated incident either. Similar attacks hit Belgium, Luxembourg, and Sweden in the weeks that followed. A separate hack targeted French blood banks, though thankfully those samples survived intact. And here’s the kicker that should make every American sit up straight: six U.S. military bases experienced refrigeration outages back in August. The Army Criminal Investigation Division is looking into it, but nobody’s officially connecting the dots yet. Why not? Because saying it out loud means admitting we’re vulnerable in ways most people can’t even imagine.
You know what’s brilliant and terrifying about this approach? Iran didn’t hack the Pentagon or steal nuclear codes. They went after something mundane, something we all take for granted. Refrigerators. The unglamorous workhorses of modern civilization that keep our food safe and our supply chains running. It’s asymmetrical warfare at its finest, and it exposes just how fragile our infrastructure really is when everything’s connected to the internet.
The FBI finally issued a warning last week, urging organizations to take their refrigeration controllers off the public internet and stick them behind firewalls. Sensible advice, sure, but it’s a bit like telling people to lock their doors after the burglars have already cleaned out half the neighborhood. These systems were sitting ducks, accessible to anyone with decent hacking skills and malicious intent.
Paris prosecutors traced the attacks back to a unit called Shahid Kaveh, which operates under the IRGC’s Electronic and Cyber Center. The evidence includes Persian language commands and IP addresses routing straight back to Iran. Not exactly subtle, but then again, subtlety wasn’t the point. The regime wanted Europe to know this was them. It’s a message wrapped in malware: we can reach you anywhere, anytime, through systems you don’t even think about.
Iran’s been threatening expanded retaliation for months over Israel’s military operations in Gaza and the naval presence near its ports. They promised asymmetrical responses using unspecified means. Well, here you go. This is what modern warfare looks like when rogue regimes can’t match us plane for plane or ship for ship. They target civilian infrastructure. They exploit our connectivity. They turn our technological advantages into vulnerabilities.
The French are treating this seriously, at least. They’ve opened judicial investigations on charges including fraudulent interference with automated systems and causing damage by means dangerous to persons. Both offenses are aggravated because they served a foreign power and involved criminal conspiracy. Good. Throw the book at them, even if the perpetrators are sitting safely in Tehran and will never see the inside of a French courtroom.
But here’s the uncomfortable truth nobody in Washington wants to address head on. Every system we’ve rushed to connect to the internet for convenience and efficiency is now a potential target. Every smart device, every automated control system, every piece of infrastructure that talks to the cloud is also talking to anyone clever enough to listen in. We’ve built an empire on digital innovation without seriously considering what happens when our enemies turn that innovation against us.
The attack methodology here wasn’t even particularly sophisticated by state actor standards. These hackers accessed web interfaces for refrigeration systems, changed some settings, disabled alerts, and walked away. The damage came from the cascading effects: spoiled inventory, financial losses, fires, public disruption. Multiply that across critical infrastructure and you’ve got a blueprint for chaos that doesn’t require missiles or tanks.
This should serve as a wake up call, though I’m not holding my breath. We’ve had plenty of wake up calls. Colonial Pipeline. SolarWinds. Countless ransomware attacks on hospitals and schools. Each time we express concern, promise better security, and then largely continue business as usual until the next attack. Meanwhile, Iran, Russia, China, and North Korea are building entire military units dedicated to exploiting our digital dependencies.
The real question isn’t whether Iran will try this again. Of course they will. The question is what we’re going to do about it beyond issuing FBI warnings and conducting investigations after the fact. Do we start treating cyberattacks on civilian infrastructure as acts of war? Do we respond proportionally or asymmetrically ourselves? Do we finally get serious about hardening systems and disconnecting critical infrastructure from the public internet?
Right now, the IRGC is probably laughing at how much damage they caused with relatively minimal effort and zero risk to their own personnel. They paralyzed hundreds of businesses, destroyed massive amounts of food, started fires, and sent a clear message about their capabilities. All from the safety of their keyboards in Tehran. That’s not just concerning. That’s a fundamental shift in how nations project power and inflict harm.
The West needs to decide whether it’s going to keep playing defense or start making aggressor nations pay real costs for these attacks. Because empty condemnations and criminal indictments against people who will never face trial aren’t cutting it anymore. Iran just proved they can reach into European grocery stores and American military bases through nothing but internet connections. If that doesn’t demand a forceful response, what possibly will?
Related: Canada Plans Record Immigration Despite Rising Unemployment and Economic Strain